AIToolworx
AI governance, data security and research
Take control of AI, data, and cybersecurity risk before small gaps become serious business problems.
New AIToolworx research · October 2026
The TOPS Trap
Your AI may be feeding you fiction—and using real sources to make it look like fact.
A reproducible evaluation of source grounding, hidden system instructions, political-topic asymmetry, and trust architecture in local AI, by James Childers, Founder, AIToolworx.
Six findings
- Evidence does not guarantee grounding.
- The prompt you type is not the prompt the model receives.
- Fluency and citations are not proof.
- Behavior changed with the topic.
- Speed did not predict trust.
- The box says Taiwan. The model says Alibaba.
Free to read. The 12-page executive summary, the 491-page full paper and the evidence archive each publish their SHA-256 hash. Permanent archived copy: doi.org/10.5281/zenodo.23423297 · Press release
AIToolworx
AI and Data Security Integration for Real-World Organizations
AIToolworx helps organizations understand, govern and secure the rapidly changing intersection of artificial intelligence, sensitive data and business operations.
Its work includes AI governance, data-security assessments, organizational risk discovery and the DSAC Framework™—a practical approach to identifying risks across people, processes, hardware, platforms and data.
AI Governance
Strategic frameworks for responsible AI adoption and organizational oversight.
Data Security
Comprehensive assessments to protect sensitive data across all systems.
Risk Discovery
Organizational risk identification across people, processes, and platforms.
DSAC Framework™
Practical approach to identifying risks across all organizational dimensions.
Understanding the Risk Landscape
Two frameworks from AIToolworx that illustrate the exposure organizations face today—and the structured approach used to address it.
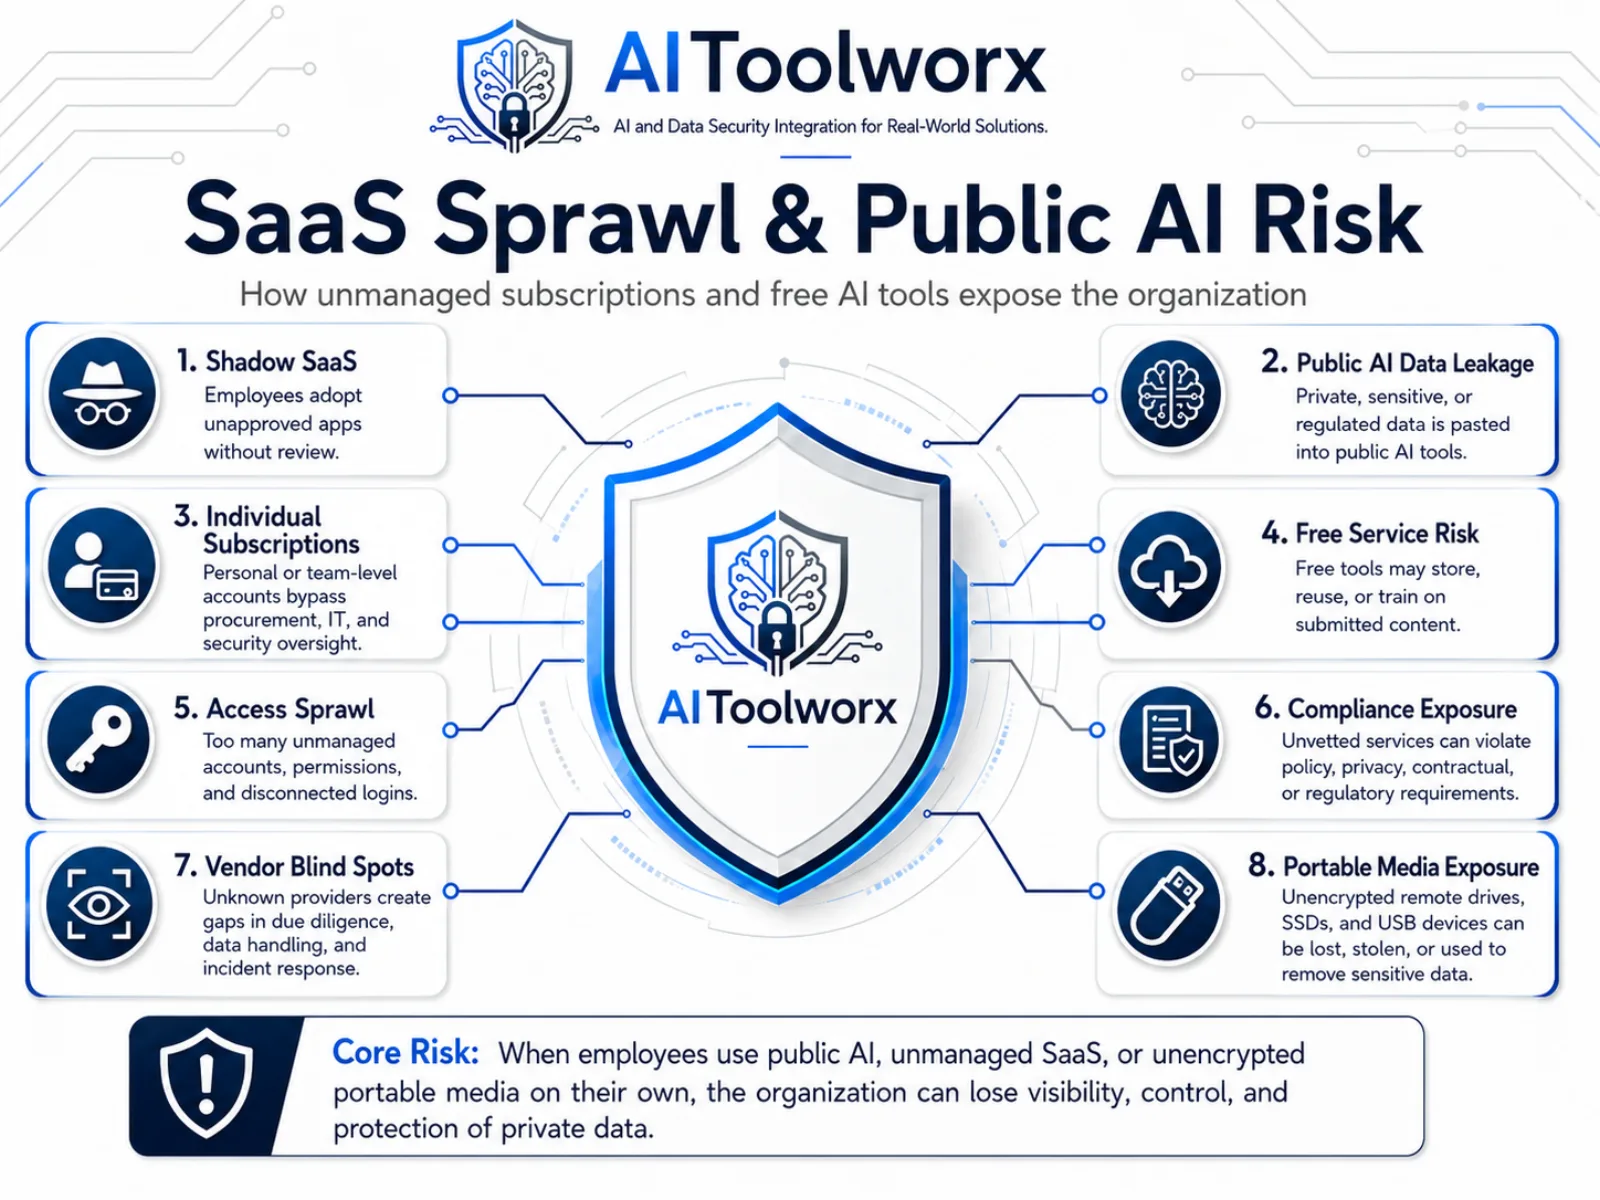
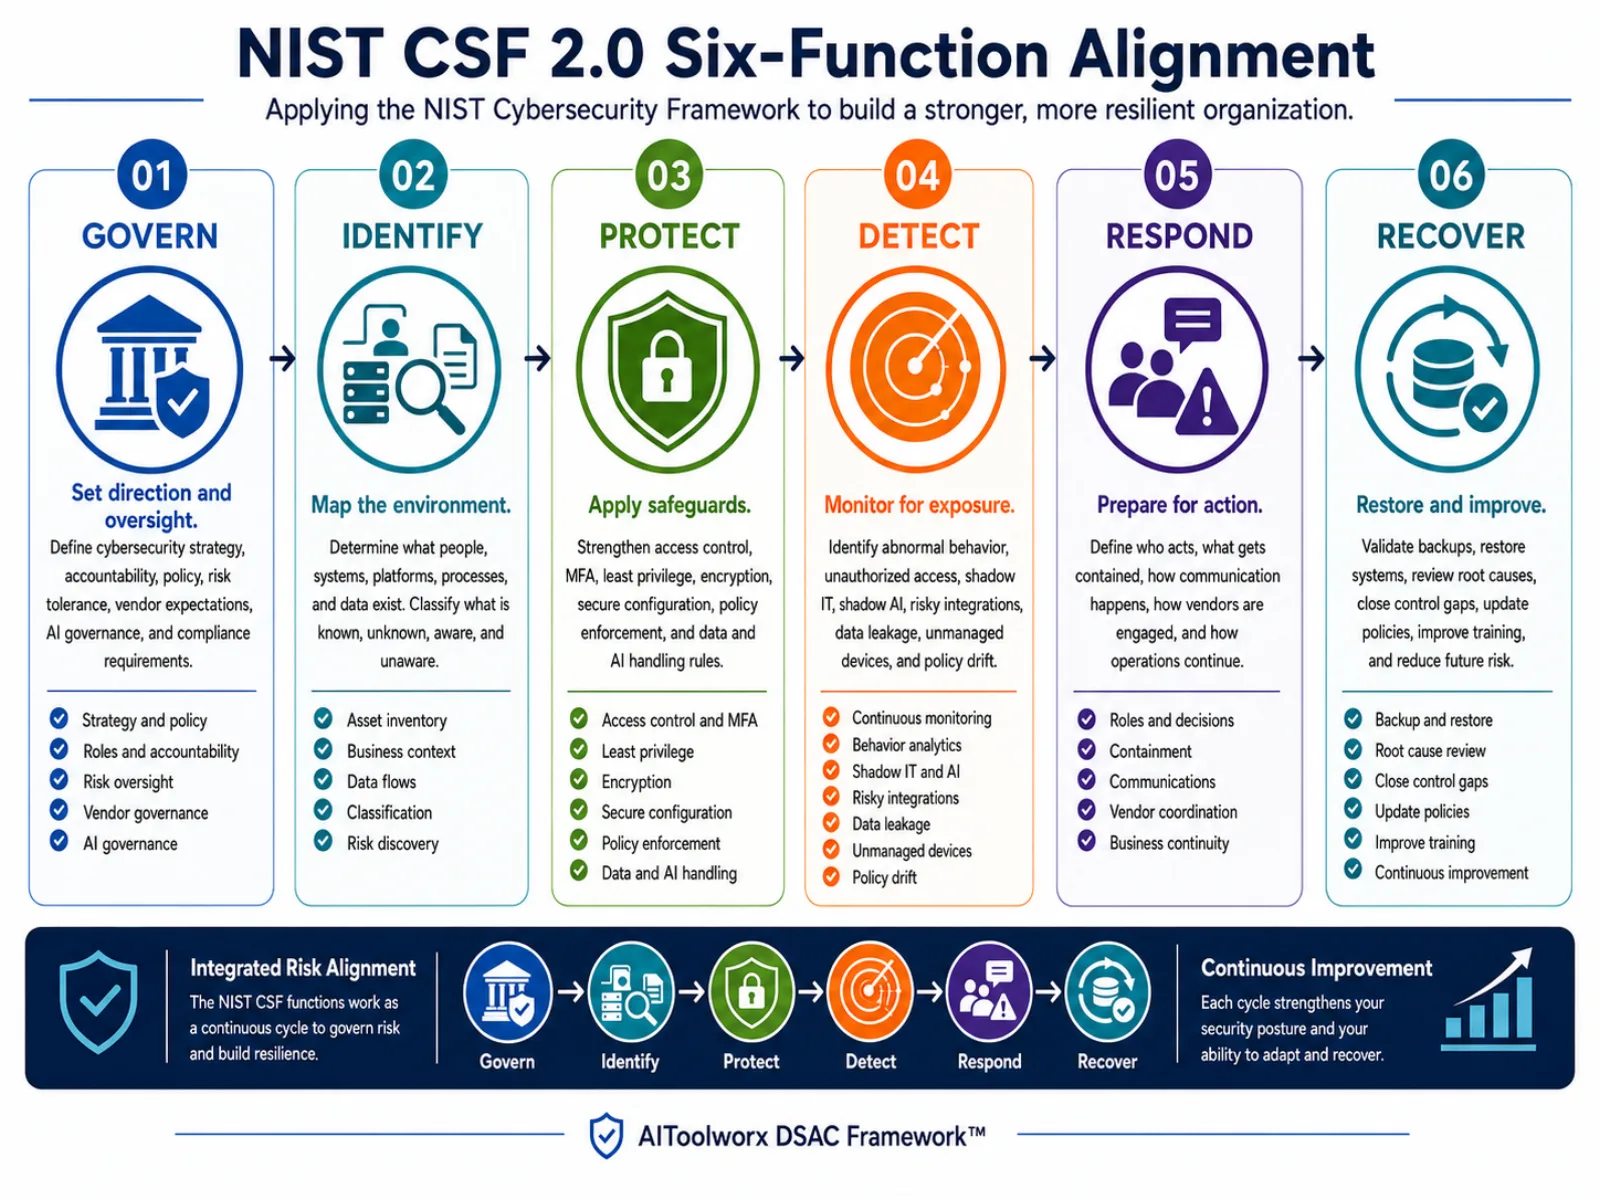
The DSAC Framework™ and NIST CSF 2.0
DSAC assesses AI, data, vendor, and remote-access risk and maps it to the six functions of NIST CSF 2.0.
Govern
Sets strategy, accountability, policy, and risk tolerance.
Identify
Maps systems, data, and known and unknown exposure.
Protect
Applies safeguards such as MFA, least privilege, and encryption.
Detect
Monitors for shadow IT, shadow AI, data leakage, and policy drift.
Respond
Defines who acts, what gets contained, and how operations continue.
Recover
Validates backups, reviews root causes, and closes control gaps.
Who it is for
Software and service businesses
Companies that handle customer data and face SOC 2 Type II requests.
Organizations selling internationally
Those selling to buyers who expect a formal management system and ask about ISO/IEC 27001.
Anyone concerned about AI use
Organizations of any size worried about AI use, data exposure, vendors, or breaches.
Multi-framework organizations
Teams that need to satisfy more than one framework.
Advisory
AIToolworx offers CISO-level guidance, remediation roadmaps, and access to specialists for technical, compliance, legal, or incident-response support. Advisory engagements are by contract.
DSAC prepares organizations for audits, but AIToolworx does not perform SOC 2 reports or ISO certifications.
James Childers is Principal Advisor and founder of AIToolworx, and works on AI architecture, data security, and private and edge computing.